Configuring the RocketCyber Syslog Collector
This article describes how to configure the Syslog Collector. The Syslog Collector is designed to aggregate threat events from third‑party vendors when the RocketCyber SOC platform does not have an existing purpose‑built integration for that vendor.
Common Event Format (CEF) and Log Extended Event Format (LEEF) are open standard Syslog formats adopted across numerous application, cloud, and hardware vendors for log management and security information interoperability.
The Syslog Collector works specifically with vendors that support Syslog CEF and LEEF log formats.
Configure the Syslog Collector
The Syslog Collector is not enabled from the App Store by default. Contact RocketCyber Support to have the Syslog Collector enabled for your organization.
Once enabled:
1. Go in context as the tenant where data will be aggregated.
-
The Syslog Collector is configured at the organization level.
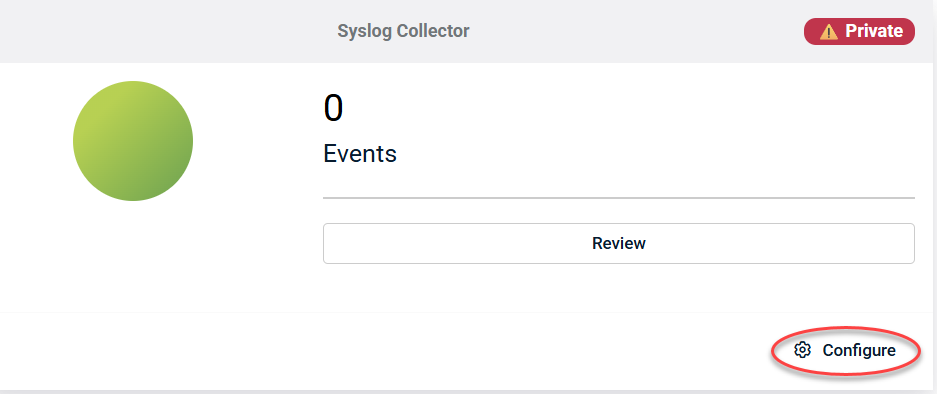
2. Click Configure to open the configuration settings.
3. In the Syslog Servers tab, select one or more devices to designate as Syslog collectors and click Create.
-
Previously limited to a single collector per organization, the Syslog Collector now supports up to 100 selected devices per organization.
-
Use the arrow controls to move devices between the Available Devices and Selected Devices lists.
-
Only Windows devices are supported as Syslog collectors.
-
A RocketAgent must already be deployed to a Windows device before configuration.
.png)
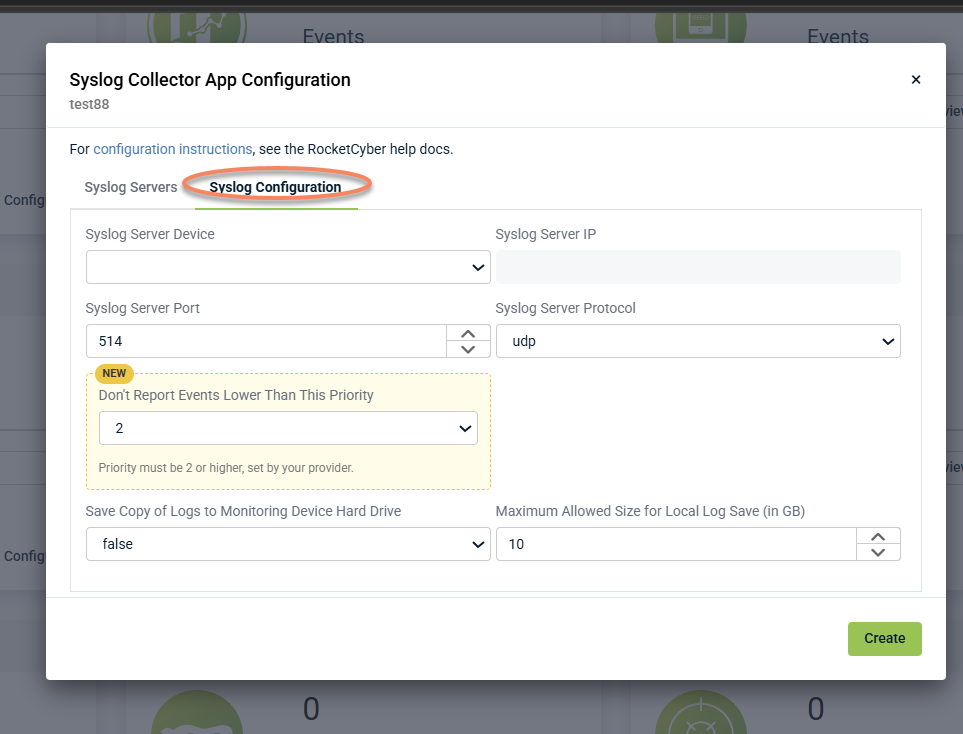
4. Use the Syslog Configuration tab to configure the selected Syslog collector devices. Available settings include the Syslog server device, IP address, port, protocol, event priority filtering, and local log storage options.
Consider the following recommendations when configuring Syslog collector devices:
-
UDP Port: The default configuration uses UDP port 514. If this port is already in use on the selected Syslog collector, change it to an unused port such as 541 or 551.
-
IP Address: When selecting a Syslog collector device, it is recommended to use a static IP address rather than DHCP to ensure consistent log forwarding.
-
Device Selection: Ensure inbound UDP traffic is permitted on the selected Syslog collector and is not blocked by firewall rules. An always-on device is recommended.
-
Event Priority Filtering: Use the Don't Report Events Lower Than This Priority setting to filter events below the selected priority threshold.
-
Local Log Storage: If you enable local log storage, configure an appropriate maximum size to avoid excessive disk usage on the Syslog collector.